Bitcoiners in the Nordics and readers of the BTCHEL newsletter The Nordic Node know full well that the Nordics are crazy-full of incredible Bitcoin authors. Kalle Rosenbaum, Ioni Appelberg, Morten Søberg etc, etc.
When Defending Bitcoin by our in-house security expert and BTCHEL programming master Luke de Wolf was published back in June, we ran a Nordic Node issue and an exclusive Q&A-type interview with him about the book. What was most astonishing was how quickly it had all come together: idea-to-print in about six months. The book has been incredibly successful, with endorsements and mentions by Jeff Booth, Lyn Alden, Lawrence Lepard and more, and has sold about 500 copies!
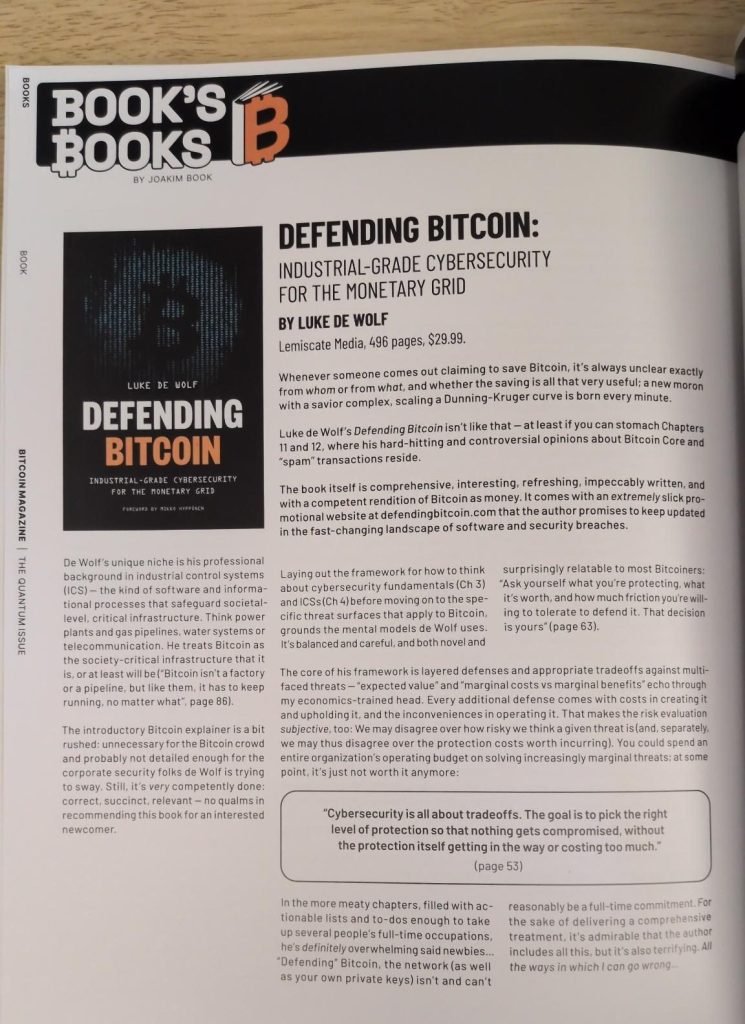
At the same time, I wrote a (slightly more critical) book review for Bitcoin Magazine’s Print magazine where my book review columns (“Book’s Books”) have more of an elegant and/or ranty feel to them.
Today, I release that one online — all 1,700 words of it! Bear with me!
The book is for sale at the Bitcoin Infinity Store (for BTC) and Amazon (dirty fiat) and most online places… if you’re in Lugano for Plan B Forum this week, it’s available there as well!
This review ran in Bitcoin Magazine Print, in the Quantum Issue (#42), the mentioning of it here was a condition for republishing. It was written in June, at the height of the BIP-110 drama and before the fork failed.
Whenever someone comes out claiming to save Bitcoin, it’s always unclear exactly from whom or from what, and whether the saving is all that very useful; a new moron with a savior complex, scaling a Dunning-Kruger curve, is born every minute.
Luke de Wolf’s Defending Bitcoin isn’t like that — at least if you can stomach Chapters 11 and 12, where his hard-hitting and controversial opinions about Bitcoin Core and “spam” transactions reside.
The book itself is comprehensive, interesting, refreshing, impeccably written, and with a competent rendition of Bitcoin as money. It comes with an extremely slick promotional website at defendingbitcoin.com that the author promises to keep updated in the fast-changing landscape of software and security breaches.
De Wolf’s unique niche is his professional background in industrial control systems (ICS) — the kind of software and informational processes that safeguard societal-level, critical infrastructure. Think power plants and gas pipelines, water systems or telecommunication. He treats Bitcoin as the society-critical infrastructure that it is, or at least will be (“Bitcoin isn’t a factory or a pipeline, but like them, it has to keep running, no matter what”, page 86).
The introductory Bitcoin explainer is a bit rushed: unnecessary for the Bitcoin crowd and probably not detailed enough for the corporate security folks de Wolf is trying to sway. Still, it’s very competently done: correct, succinct, relevant — no qualms in recommending this book for an interested newcomer.
Laying out the framework for how to think about cybersecurity fundamentals (Ch 3) and ICSs (Ch 4) before moving on to the specific threat surfaces that apply to Bitcoin, grounds the mental models de Wolf uses. It’s balanced and careful, and both novel and surprisingly relatable to most Bitcoiners: “Ask yourself what you’re protecting, what it’s worth, and how much friction you’re willing to tolerate to defend it. That decision is yours” (page 63).
The core of his framework is layered defenses and appropriate tradeoffs against multifaceted threats — “expected value” and “marginal costs vs marginal benefits” echo through my economics-trained head. Every additional defense comes with costs in creating it and upholding it, and the inconveniences in operating it. That makes the risk evaluation subjective, too: We may disagree over how risky we think a given threat is (and, separately, we may thus disagree over the protection costs worth incurring). You could spend an organization’s entire operating budget on solving increasingly marginal threats; at some point, it’s just not worth it anymore:
“Cybersecurity is all about tradeoffs. The goal is to pick the right level of protection so that nothing gets compromised, without the protection itself getting in the way or costing too much” (page 53)
In the more meaty chapters, filled with actionable lists and to-dos enough to take up several people’s full-time occupations, he’s definitely overwhelming said newbies… “Defending” Bitcoin, the network (as well as your own private keys) isn’t and can’t reasonably be a full-time commitment. For the sake of delivering a comprehensive treatment, it’s admirable that the author includes all this, but it’s also terrifying. All the ways in which I can go wrong…
Hyperbolic Contradictions Won’t Rug the Spammers
The arguments for either side of the broad schism running through Core-Knots, arbitrary data, mining (template) centralization, and node settings are presented competently and succinctly, only occasionally misleading. To de Wolf’s credit, they’re portrayed miles better than the often performative mudslinging we’re used to from Twitter or conference stages. This is the best possible version of the argument; whatever your stance on quantum, Bitcoin Core, Knots, or nonmonetary data on Bitcoin, Defending Bitcoin is the bright, shining star for considering these themes.
De Wolf definitely goes too far at times, and he’s repeatedly too shilly for Knots and OCEAN.
He plays fast and loose with “fungibility”, implying that anything impinging on one UTXO’s interchangeability with another undermines its use as money: “[I]f ‘clean’ Bitcoin spends freely while ‘tainted’ Bitcoin gets stuck in limbo, it stops working as money” (page 207). Gold and fiat, two rival monetary systems, have performed their monetary functions reasonably well, even with quite a lot of obstacles to their global fungibility.
It’s true that Bitcoin’s don’t trust, verify ethos is meaningfully different than “every other monetary system [where] someone else decides what’s valid.” But it’s hyperbolic to conclude that unless a user runs a node, “everything above it works from a lie” (page 225). There’s a sliding scale of trust, the ease with which you could verify transactions and keys via other means and, in consequence, the vast number of unconnected, somewhat-trusted people around.
De Wolf’s rundown of Ordinals, NFTs, and the OP_RETURN debacle happens in Chapter 11 (ironically, since some would consider these themes pretty bankrupt…). He admits that these “unwanted” components of Bitcoin are impossible to stop: “It’s always been possible to embed data on Bitcoin” (page 250), that “Bitcoin’s technical properties mean that anyone can embed arbitrary data through known means at any time” (page 263), and that “voluntary filtering alone can’t solve it” (page 263). He nevertheless spends the entire chapter assembling all the reasons nonmonetary data on Bitcoin is bad (“an abuse of a monetary network”, page 265), and recommends users running Knots to ever-so-marginally prevent these transactions relaying across the network: “Relay filtering through Knots is a preventative control that stops spam from propagating through your node” (page 265), and “Mining on a spam-filtering pool or with your own template is the surest way to keep non-financial data out of blocks” (page 264).
The fact that these efforts are individually expensive and inconvenient, yet practically achieve nothing, should not detract from the noble fight against spam:
“In cybersecurity, we don’t stop putting up defenses just because an adversary is hard to stop. It may be impossible to completely stop arbitrary data on Bitcoin, but it’s absolutely possible to slow it down, force it into more difficult or more expensive vectors, and generally to repudiate it as a legitimate use of Bitcoin” (pages 262-63).
De Wolf paints himself into a corner by admitting repeatedly that arbitrary data is impossible to stop, but that somehow it’s still incredibly important that you — yes, you! — do everything in your power to microscopically close this devastating hack.
In these more controversial chapters, he straddles the line between dispassionate analyst and activist with a cause. The calls to individual action, no matter how minuscule or impotent, are entirely detached from the careful balancing of costs and benefits from the early portions of the book. “[D]on’t let convenience override the integrity of the system you’re protecting” (page 254), he writes, forgetting that “Low-impact things that don’t matter much aren’t worth considering” (page 55).
In critiquing Core changes, he writes that “Bitcoin isn’t an engineering project with a single set of design goals” (page 283) — a statement in stark contrast with the money-only, Bitcoin “maximalism” thesis that runs through the book. The segments attacking “arbitrary data abuse” as “unauthorized non-process traffic flooding the Level 0 network” (page 256) seem pretty clear on what Bitcoin is supposed to be and for whom it works.
Every sort of counterargument here relies on what Bitcoin intends, what Satoshi meant for Bitcoin to be, and what the ultimate purpose of the network is. We can disagree about the answers to these questions, but the point is that they’re subjective, ambiguous, and mostly unanswerable — meaning that arguments based on an interpretation of what Bitcoin is supposed to be become just that: hypothetical, subjective conjectures.
In the name of countering spam/inscriptions/unwanted data, getting rid of consensus-valid transactions isn’t worth it. I suspect de Wolf reluctantly understands that — which is why his recommendations boil down to tame, virtue-signaling individual-level actions. Feeling good, not doing (much?) good.
“Whether BIP 110 specifically is the right vehicle to address arbitrary data remains an open question. I’m clear in my position that arbitrary data is not good for Bitcoin, but changing the consensus rules in a way that breaks existing functionality is a drastic step” (page 293).
In an altogether characteristic moderation, he relaxes his position with a look to chain splits — the nuclear option making most drastic proposals to counter “spam” not worth it.
What annoys me the most is the presumption that arbitrary data is infinitely profitable, thus is (or will) crowd out bitcoin’s monetary use — an existential plague rather than a mostly harmless phenomenon at the, uh, uncharted backwaters of the unfashionable end of the western spiral arm of the Galaxy…
“Spammers aren’t using Bitcoin as money. Rather, they’re using it as a way to generate value for themselves through the data they embed. It’s worth it to them to pay the fee to get their data inscribed on Bitcoin, and presumably they expect to make their money back” (page 260).
Call me blue-eyed, I just don’t believe there’s a constant, ever-lasting demand for worthless digital junk. Besides, in manias and bubbles, that sort of leaning-against-the-wind never works — in part because people (irrationally) hoping to profit from peddling nonsense think they’ll profit so much that whatever tiny obstacles you place in their path are but a nuisance. The kicker is that they won’t; thus, the existence of a final sucker.
The security assessment that the book constitutes, complete with ratings and urgency, is terrifying but also probably long overdue for a leaderless monetary project. It’s admirable that the author created a comprehensive, actionable guide for all the ways you can defend B(b)itcoin. But “Defending” Bitcoin, the network and your own stash, can’t reasonably be a full-time job. What was supposed to be an exit from a part-time investment job outperforming inflation became, implicitly, a part-time technical job staying up to date in software maintenance, running a Lightning node, juggling multisig keys for self-custody assurance, running multiple node implementations, and constructing block templates from your solar-powered BitAxe.
The final, optimistic takeaway is that this deep dive made de Wolf see Bitcoin as more resilient than he first supposed. Despite outlining dozens of threats, across AI and quantum and spammers and poor key management and colluding miners and faulty privacy and hostile governments, de Wolf’s “assertion is that Bitcoin has held up remarkably well” (page 383). The downside is that we are its security team.
It’s a beautiful summary of a painstaking journey, with lots left to do. The repeated emphasis on balancing convenience and security lingers.
SELECTED QUOTES:
- “In every system I’ve ever worked on, the most common failure wasn’t a sophisticated attack. It was a human mistake” (pages 389-90).
- “In 2017, Core had defended Bitcoin’s monetary properties against outside pressure. In 2025, it was telling the community that disagreement would have to express itself somewhere else” (pages 280-81).
- “Quantum threatens the cryptographic assumptions that protect keys and secure mining. AI threatens the human and economic layer around the protocol, from development and social engineering to mining economics” (page 360).
- “The protocol doesn’t defend itself. People defend it through the choices they make about what software to run, what development to fund, and what behavior to tolerate” (page 298).