Kategoria: Books

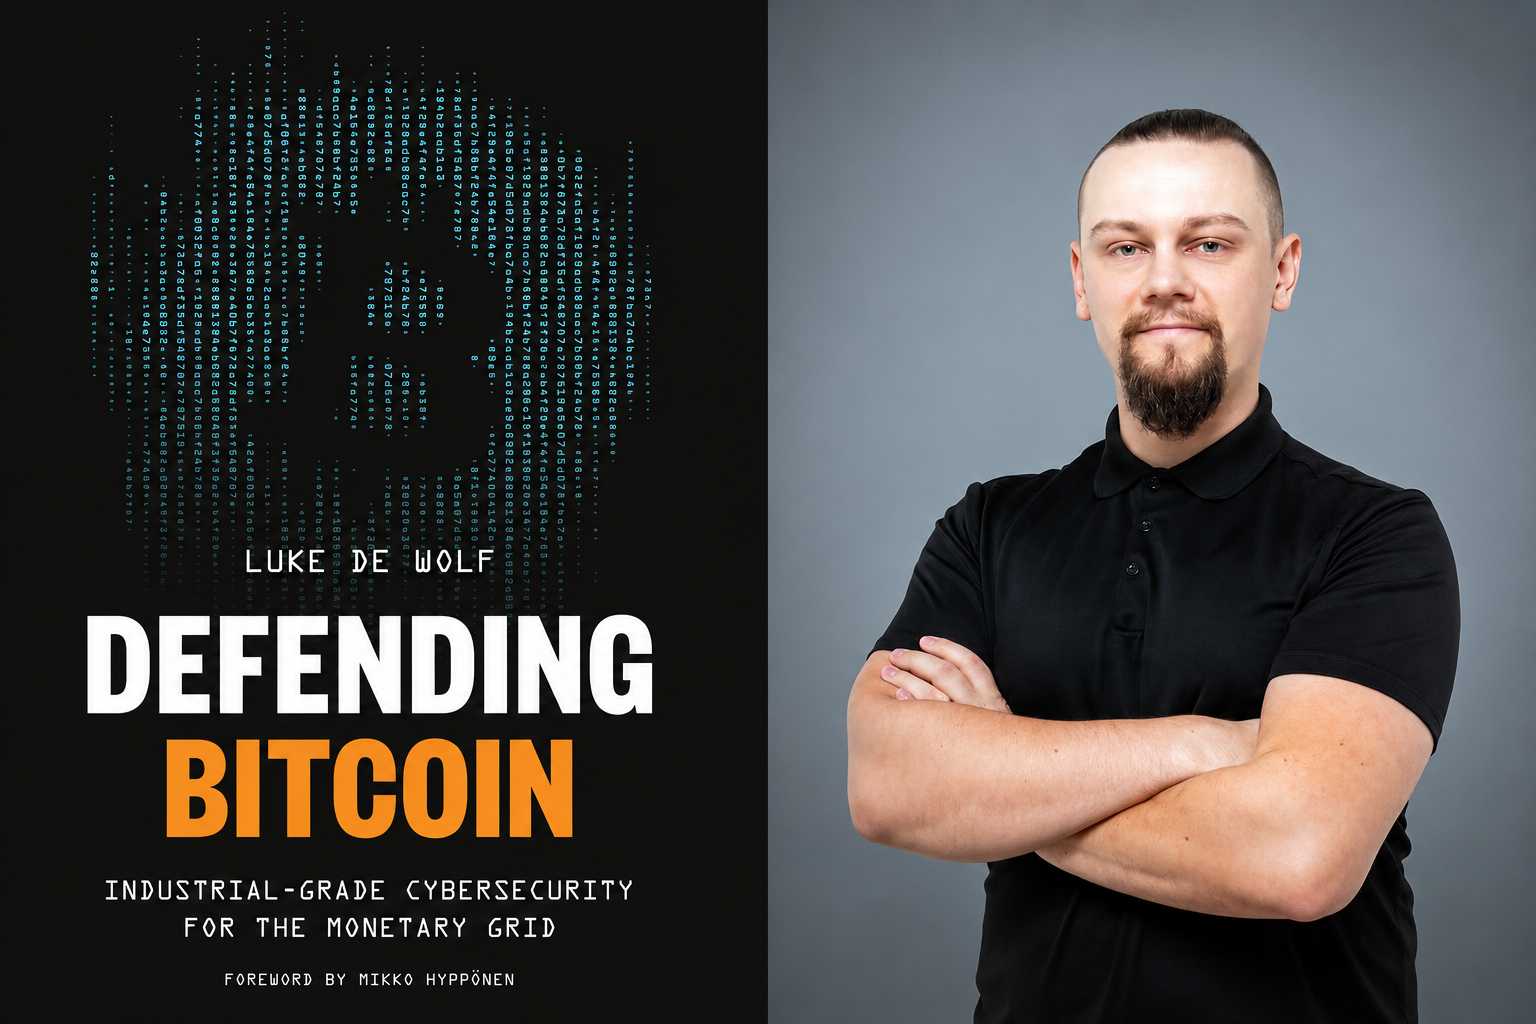
  • Reviewing “Defending Bitcoin” by Luke de Wolf

    Reviewing “Defending Bitcoin” by Luke de Wolf

    Bitcoiners in the Nordics and readers of the BTCHEL newsletter The Nordic Node know full well that the Nordics are crazy-full of incredible Bitcoin authors. Kalle Rosenbaum, Ioni Appelberg, Morten Søberg etc, etc.


    When Defending Bitcoin by our in-house security expert and BTCHEL programming master Luke de Wolf was published back in June, we ran a Nordic Node issue and an exclusive Q&A-type interview with him about the book. What was most astonishing was how quickly it had all come together: idea-to-print in about six months. The book has been incredibly successful, with endorsements and mentions by Jeff Booth, Lyn Alden, Lawrence Lepard and more, and has sold about 500 copies!

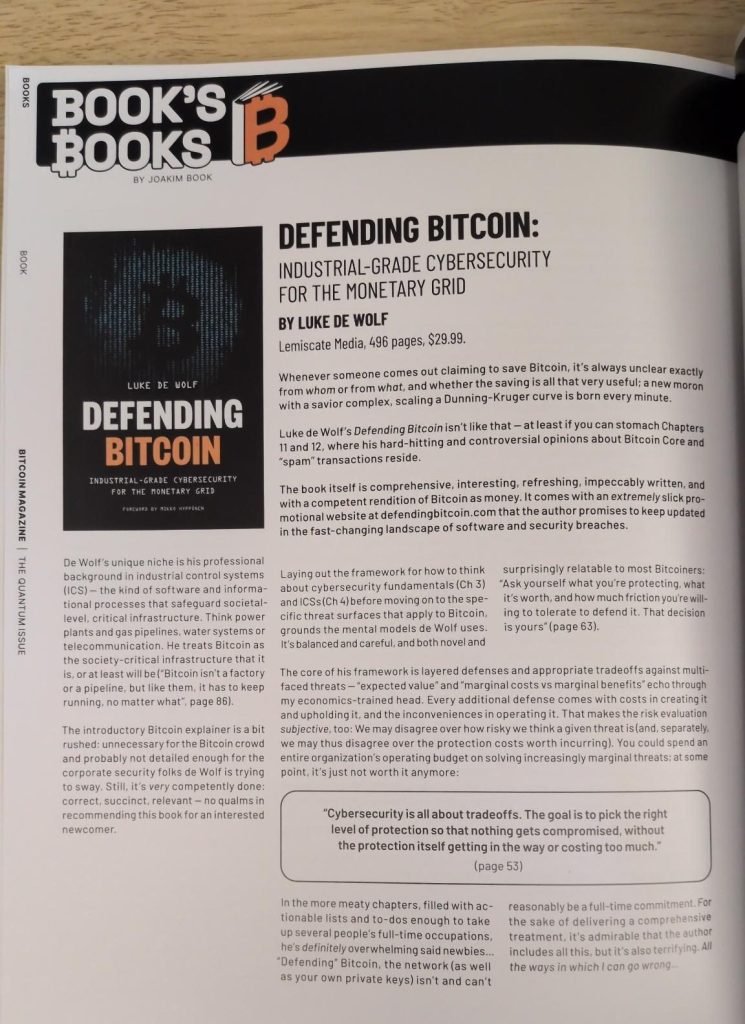
    At the same time, I wrote a (slightly more critical) book review for Bitcoin Magazine’s Print magazine where my book review columns (“Book’s Books”) have more of an elegant and/or ranty feel to them.

    Today, I release that one online — all 1,700 words of it! Bear with me!


    The book is for sale at the Bitcoin Infinity Store (for BTC) and Amazon (dirty fiat) and most online places… if you’re in Lugano for Plan B Forum this week, it’s available there as well!


    This review ran in Bitcoin Magazine Print, in the Quantum Issue (#42), the mentioning of it here was a condition for republishing. It was written in June, at the height of the BIP-110 drama and before the fork failed.


    Whenever someone comes out claiming to save Bitcoin, it’s always unclear exactly from whom or from what, and whether the saving is all that very useful; a new moron with a savior complex, scaling a Dunning-Kruger curve, is born every minute.


    Luke de Wolf’s Defending Bitcoin isn’t like that — at least if you can stomach Chapters 11 and 12, where his hard-hitting and controversial opinions about Bitcoin Core and “spam” transactions reside.


    The book itself is comprehensive, interesting, refreshing, impeccably written, and with a competent rendition of Bitcoin as money. It comes with an extremely slick promotional website at defendingbitcoin.com that the author promises to keep updated in the fast-changing landscape of software and security breaches.

    De Wolf’s unique niche is his professional background in industrial control systems (ICS) — the kind of software and informational processes that safeguard societal-level, critical infrastructure. Think power plants and gas pipelines, water systems or telecommunication. He treats Bitcoin as the society-critical infrastructure that it is, or at least will be (“Bitcoin isn’t a factory or a pipeline, but like them, it has to keep running, no matter what”, page 86).


    The introductory Bitcoin explainer is a bit rushed: unnecessary for the Bitcoin crowd and probably not detailed enough for the corporate security folks de Wolf is trying to sway. Still, it’s very competently done: correct, succinct, relevant — no qualms in recommending this book for an interested newcomer. 


    Laying out the framework for how to think about cybersecurity fundamentals (Ch 3) and ICSs (Ch 4) before moving on to the specific threat surfaces that apply to Bitcoin, grounds the mental models de Wolf uses. It’s balanced and careful, and both novel and surprisingly relatable to most Bitcoiners: “Ask yourself what you’re protecting, what it’s worth, and how much friction you’re willing to tolerate to defend it. That decision is yours” (page 63).

    The core of his framework is layered defenses and appropriate tradeoffs against multifaceted threats — “expected value” and “marginal costs vs marginal benefits” echo through my economics-trained head. Every additional defense comes with costs in creating it and upholding it, and the inconveniences in operating it. That makes the risk evaluation subjective, too: We may disagree over how risky we think a given threat is (and, separately, we may thus disagree over the protection costs worth incurring). You could spend an organization’s entire operating budget on solving increasingly marginal threats; at some point, it’s just not worth it anymore:

    “Cybersecurity is all about tradeoffs. The goal is to pick the right level of protection so that nothing gets compromised, without the protection itself getting in the way or costing too much” (page 53)

    In the more meaty chapters, filled with actionable lists and to-dos enough to take up several people’s full-time occupations, he’s definitely overwhelming said newbies… “Defending” Bitcoin, the network (as well as your own private keys) isn’t and can’t reasonably be a full-time commitment. For the sake of delivering a comprehensive treatment, it’s admirable that the author includes all this, but it’s also terrifying. All the ways in which I can go wrong…

    Hyperbolic Contradictions Won’t Rug the Spammers


    The arguments for either side of the broad schism running through Core-Knots, arbitrary data, mining (template) centralization, and node settings are presented competently and succinctly, only occasionally misleading. To de Wolf’s credit, they’re portrayed miles better than the often performative mudslinging we’re used to from Twitter or conference stages. This is the best possible version of the argument; whatever your stance on quantum, Bitcoin Core, Knots, or nonmonetary data on Bitcoin, Defending Bitcoin is the bright, shining star for considering these themes.

    De Wolf definitely goes too far at times, and he’s repeatedly too shilly for Knots and OCEAN.

    He plays fast and loose with “fungibility”, implying that anything impinging on one UTXO’s interchangeability with another undermines its use as money: “[I]f ‘clean’ Bitcoin spends freely while ‘tainted’ Bitcoin gets stuck in limbo, it stops working as money” (page 207). Gold and fiat, two rival monetary systems, have performed their monetary functions reasonably well, even with quite a lot of obstacles to their global fungibility.

    It’s true that Bitcoin’s don’t trust, verify ethos is meaningfully different than “every other monetary system [where] someone else decides what’s valid.” But it’s hyperbolic to conclude that unless a user runs a node, “everything above it works from a lie” (page 225). There’s a sliding scale of trust, the ease with which you could verify transactions and keys via other means and, in consequence, the vast number of unconnected, somewhat-trusted people around.

    De Wolf’s rundown of Ordinals, NFTs, and the OP_RETURN debacle happens in Chapter 11 (ironically, since some would consider these themes pretty bankrupt…). He admits that these “unwanted” components of Bitcoin are impossible to stop: “It’s always been possible to embed data on Bitcoin” (page 250), that “Bitcoin’s technical properties mean that anyone can embed arbitrary data through known means at any time” (page 263), and that “voluntary filtering alone can’t solve it” (page 263). He nevertheless spends the entire chapter assembling all the reasons nonmonetary data on Bitcoin is bad (“an abuse of a monetary network”, page 265), and recommends users running Knots to ever-so-marginally prevent these transactions relaying across the network: “Relay filtering through Knots is a preventative control that stops spam from propagating through your node” (page 265), and “Mining on a spam-filtering pool or with your own template is the surest way to keep non-financial data out of blocks” (page 264).

    The fact that these efforts are individually expensive and inconvenient, yet practically achieve nothing, should not detract from the noble fight against spam: 

    “In cybersecurity, we don’t stop putting up defenses just because an adversary is hard to stop. It may be impossible to completely stop arbitrary data on Bitcoin, but it’s absolutely possible to slow it down, force it into more difficult or more expensive vectors, and generally to repudiate it as a legitimate use of Bitcoin” (pages 262-63).


    De Wolf paints himself into a corner by admitting repeatedly that arbitrary data is impossible to stop, but that somehow it’s still incredibly important that you — yes, you! — do everything in your power to microscopically close this devastating hack.

    In these more controversial chapters, he straddles the line between dispassionate analyst and activist with a cause. The calls to individual action, no matter how minuscule or impotent, are entirely detached from the careful balancing of costs and benefits from the early portions of the book. “[D]on’t let convenience override the integrity of the system you’re protecting” (page 254), he writes, forgetting that “Low-impact things that don’t matter much aren’t worth considering” (page 55). 

    In critiquing Core changes, he writes that “Bitcoin isn’t an engineering project with a single set of design goals” (page 283) — a statement in stark contrast with the money-only, Bitcoin “maximalism” thesis that runs through the book. The segments attacking “arbitrary data abuse” as “unauthorized non-process traffic flooding the Level 0 network” (page 256) seem pretty clear on what Bitcoin is supposed to be and for whom it works.

    Every sort of counterargument here relies on what Bitcoin intends, what Satoshi meant for Bitcoin to be, and what the ultimate purpose of the network is. We can disagree about the answers to these questions, but the point is that they’re subjective, ambiguous, and mostly unanswerable — meaning that arguments based on an interpretation of what Bitcoin is supposed to be become just that: hypothetical, subjective conjectures.

    In the name of countering spam/inscriptions/unwanted data, getting rid of consensus-valid transactions isn’t worth it. I suspect de Wolf reluctantly understands that — which is why his recommendations boil down to tame, virtue-signaling individual-level actions. Feeling good, not doing (much?) good.

    “Whether BIP 110 specifically is the right vehicle to address arbitrary data remains an open question. I’m clear in my position that arbitrary data is not good for Bitcoin, but changing the consensus rules in a way that breaks existing functionality is a drastic step” (page 293).

    In an altogether characteristic moderation, he relaxes his position with a look to chain splits — the nuclear option making most drastic proposals to counter “spam” not worth it. 

    What annoys me the most is the presumption that arbitrary data is infinitely profitable, thus is (or will) crowd out bitcoin’s monetary use — an existential plague rather than a mostly harmless phenomenon at the, uh, uncharted backwaters of the unfashionable end of the western spiral arm of the Galaxy…

    “Spammers aren’t using Bitcoin as money. Rather, they’re using it as a way to generate value for themselves through the data they embed. It’s worth it to them to pay the fee to get their data inscribed on Bitcoin, and presumably they expect to make their money back” (page 260).

    Call me blue-eyed, I just don’t believe there’s a constant, ever-lasting demand for worthless digital junk. Besides, in manias and bubbles, that sort of leaning-against-the-wind never works — in part because people (irrationally) hoping to profit from peddling nonsense think they’ll profit so much that whatever tiny obstacles you place in their path are but a nuisance. The kicker is that they won’t; thus, the existence of a final sucker.

    The security assessment that the book constitutes, complete with ratings and urgency, is terrifying but also probably long overdue for a leaderless monetary project. It’s admirable that the author created a comprehensive, actionable guide for all the ways you can defend B(b)itcoin. But “Defending” Bitcoin, the network and your own stash, can’t reasonably be a full-time job. What was supposed to be an exit from a part-time investment job outperforming inflation became, implicitly, a part-time technical job staying up to date in software maintenance, running a Lightning node, juggling multisig keys for self-custody assurance, running multiple node implementations, and constructing block templates from your solar-powered BitAxe. 

    The final, optimistic takeaway is that this deep dive made de Wolf see Bitcoin as more resilient than he first supposed. Despite outlining dozens of threats, across AI and quantum and spammers and poor key management and colluding miners and faulty privacy and hostile governments, de Wolf’s “assertion is that Bitcoin has held up remarkably well” (page 383). The downside is that we are its security team.

    It’s a beautiful summary of a painstaking journey, with lots left to do. The repeated emphasis on balancing convenience and security lingers.

    SELECTED QUOTES:

    • “In every system I’ve ever worked on, the most common failure wasn’t a sophisticated attack. It was a human mistake” (pages 389-90).
    • “In 2017, Core had defended Bitcoin’s monetary properties against outside pressure. In 2025, it was telling the community that disagreement would have to express itself somewhere else” (pages 280-81).
    • “Quantum threatens the cryptographic assumptions that protect keys and secure mining. AI threatens the human and economic layer around the protocol, from development and social engineering to mining economics” (page 360).
    • “The protocol doesn’t defend itself. People defend it through the choices they make about what software to run, what development to fund, and what behavior to tolerate” (page 298).
  • Ioni Appelberg and Abundance Through Scarcity: Civilization and Space

    Ioni Appelberg and Abundance Through Scarcity: Civilization and Space

    The first time I read Ioni Appelberg’s great Abundance Through Scarcity was in a D.C. hotel restaurant at the height of the last bull market. It felt celebratory and appropriately lifted my gaze from the depravity of that lost, despicable, politicized city. Money is civilization; civilization is energy; energy propels us forward, technically, and outward, spatially. Our destiny is to become a space-faring nation — or to perish.


    Because I’m different, the times are different, and Ioni actually updated and revamped the book this year (meaning the book itself is different), it’s hard to tell exactly why reading Abundance this time around is an altogether different experience.

    It still has the same lift-your-goddamn-gaze flavor. It’s still obsessed with space and human civilization — quite often the Roman one. It still celebrates money as this insane, improbable, incredible cooperative device between humans. It’s the silent patchwork/bind knitting us together as a species, as a civilization, as the economic collaboration that is the world economy. That the cover is a Bitcoin-clad Astronaut battling a space storm on some far-off planet is strange and unconventional, until you realize that Ioni is obsessed with humans — as a global civilization — becoming a space-faring species.


    But fiat, and its increasingly broken and collapsing institutions, were not meant for the space age. “Fiat currency evolved for a different world,” (p. 227) i.e., our national (often centrally directed) economies, where coordination horizons remain short. For bigger, solar-system endeavors, we need something else:

    “Trying to run a planetary civilization on institution-bound money is like trying to stream video over a fax machine. The infrastructure is not built for what we are trying to do.” (p. 227).


    Then again, Bitcoin with its ten-minute block times would struggle as intergalactic or even galactic money: It’s too slow, the light years of distance between planets and solar systems in our galaxy too vast. Mars, let alone the moon, will probably resort to their own chains.


    The Most Important Thing Satoshi Gave Us


    Scarcity. True, unfakeable, unrivalled scarcity: “scarcity that does not depend on geology or engineering. Mathematical scarcity” (p. 103). Up until Satoshi unleashed Bitcoin on the world, everything digital was infinitely copiable. Nothing (but immediately accessible, material things) was truly ownable. The white paper’s great disruption was

    “…a side effect of making one thing abundant that had previously been scarce: the ability to move value without permission” (p. 150).


    What I saw this time reading the revamped Abundance was an urgency I didn’t notice last time. We are running out of time.


    The rhetorical twists he uses hit like gut punches. Voyager, the hopeful satellites we (“we”) sent out at the peak of the space race, were filled with human language, whale songs, art, and some small collection of the best of what we are. Sent out for an unknown future and improbable meeting, it “keeps going, unchanged, because it was built at a moment when civilization still believed in tomorrow….

    We are the ones who stopped.”


    Abundance is mostly a hopeful book, the way Ioni strikes me as a hopeful, kind soul. It asks the reader to lift their gaze and consider human life and existence on a larger scale, on a longer time frame, doing something more important than your everyday life. And if it hits right, it asks the reader to work diligently for civilization’s success and thriving instead of its decline.  

    It’s also a doomerist, terrifying story — reminding us that what we’re doing here in Bitcoinland is much more important than number-go-up or preserving wealth from the value erosion that is money printing and inflation.


    Bitcoin is here and works, but the wider public remains mostly ignorant of it — if not outright hostile. This is the sort of goldbug/black-pilled/Austrian doomerism I can get behind… fiat can, if not thrive and flourish, muddle through much longer than anyone thinks reasonable.


    This has to work soon, or else (Western) civ is quite rapidly circling the drains.


    Abundance through scarcity sounds like a contradiction — until you realize that some (most?) of the greatest things humanity ever achieved happened by taking away rather than adding; adding by subtraction. Via Negativa. Or, in the overarching metaphor of the book itself: Michelangelo saw — so goes the apocryphal story, anyway — his masterpiece marble sculpture “David” in a piece of inferior block, rejected by everyone else as unsuitable for crafting anything. Just take away everything that isn’t David.


    Toward the very end of the book, Ioni speculates once more on the great filtering and the Fermi paradox (which I was told recently by someone working for NASA, was haphazardly written on a napkin and should be considered accordingly) that “Perhaps the Great Silence is filled with worlds that mastered energy, computation, and intelligence, yet never learned how to endure” (p. 245).

    “The record persists, waiting to see whether it will become the backbone of a conversation across thousands of generations, or a root or in the ruins of another failed ascent” (p. 246).


    This week, you’ll find Ioni giving a lecture on Bitcoin and longevity on Friday exclusively for the OG stage, and be part of the main stage panel session on “Sauna, Meat, and Sun: Bitcoin meets Biohackers” on Saturday.

  • Defending Bitcoin: An Exclusive Interview with Luke de Wolf

    Defending Bitcoin: An Exclusive Interview with Luke de Wolf

    And so the time has come. Let the Nordic authoring dominance proceed!

    For months, Luke de Wolf, co-founder and head of programming for BTCHEL, labored over precisely how his view of Bitcoin security was different.

    And next week, June 15, the book is out. Defending Bitcoin: Industrial-Grade Cybersecurity for the Monetary Grid is bound to be one of the most noteworthy Bitcoin books of the year.  


    It’s a serious, deeply considered security investigation of Bitcoin. Coming from an industrial control system point of view, Luke lays out a framework for thinking about threats and then spends ten ridiculously well-researched and balanced chapters investigating everything from quantum to arbitrary data, mining centralization, key management and physical security.

    I caught up with Luke and asked him a bunch of questions I hoped nobody had asked him before. Here’s a lightly edited transcript of our interview.


    JB: What was the most surprising thing you learned or discovered during the process of writing and researching the book?

    LW: I really had to get up to speed with a lot of low-level technical aspects of Bitcoin.

    I went back and reread Mastering Bitcoin [by Andreas Antonopoulos], but that was a bit hard to follow. I then read Grokking Bitcoin and Bitcoin Development Philosophy by Kalle Rosenbaum. (Those would be my top picks for someone to understand the technical side of Bitcoin, although Grokking could use an update to reflect the latest protocol changes…)


    I even took the Saving Satoshi challenge put on by Chaincode, which forced me to dust off my programming skills and do real Python coding. I learned a lot through the process, and I made it all the way to the end, with the invite to the BOSS challenge as my reward. Time commitments, not the least of which being this book, prevented me from taking the process further, but the experience was interesting and enlightening.

    I would say that the area I learned the most was in Bitcoin Script, where I had a rough understanding from Twitter discourse but hadn’t really gotten my hands dirty before.


    “After writing the book, I feel confident that I understand the whole area a lot more, and I can speak more confidently about controversial scripting changes.”

    JB: How did the idea for the book come to you? I wanna recall JK Rowling describing how the story of Harry Potter just suddenly flooded her mind, fully formed and all at once. Did you have a similar revelation with Defending Bitcoin, or was, perhaps, the constant arguing with people on Twitter last year involved in coaching it out of you?

    LW: This was an “aha” moment. I had been arguing about BIP-110 with a few prominent people, but one conversation with Stephan Livera specifically sparked the whole idea for Defending Bitcoin. I realized that I had been advocating against arbitrary data because of the same principles that govern critical infrastructure security, and everything basically fell into place. I knew exactly what kind of book I wanted to write, immediately.


    I knew I would need to build a base of vocabulary and introduce both Bitcoin and cybersecurity, and from there talk about the threats to Bitcoin and the ways to defend against those threats. I reordered two chapters and changed the contents of one after building the initial outline. That was two weeks after the initial idea.


    JB: What have you changed your mind about in writing the book?


    LW: I changed my mind about BIP-110.

    Not about the content of the change: I remain adamant that BIP-110 would be a positive thing for Bitcoin. I assert throughout Defending Bitcoin that the tradeoff to security is convenience, or, put more plainly, that every decision has tradeoffs.

    I find the technical restrictions demanded by BIP-110 to be extremely reasonable. Developers have to operate within a slightly more restrictive environment, temporarily. I don’t find that outcome to be unacceptable.

    My opposition came through writing the chapter on Governance issues, which you might think, initially, would just entrench my view that something is rotten in Bitcoin Core, and something needs to be done at all costs. It’s the last part that I realized I don’t agree with.


    “The chaos of a fork scenario is something we can’t predict.”

    I wrote a book about risk management. I realized that I couldn’t simultaneously advocate for risk reduction in every other area of Bitcoin and advocate for a fork that doesn’t have overwhelming node consensus. I had to be honest with myself and give up a position that I had been holding for months. But, I think, if you read the book you’ll see why I came to the conclusion I did.

    That’s not to say that I wouldn’t be happy if BIP-110 were to activate. Currently, I just don’t see it activating smoothly. Without node consensus, miners effectively get to choose the outcome, and I don’t see a path to sufficient hashrate for the fork. Again, the node consensus is the issue.

    If 90%+ of nodes supported BIP-110, it would be hard for miners to justify not signaling for the fork. As it stands, the numbers are quite a bit lower. It’s not about the merits of BIP-110. I just think they’re fighting a losing battle, and, from a risk reduction perspective, I can’t support it.


    JB: Do you have a favorite phrase or sentence from the book?


    LW: There’s always something you can do.


    It was important for me to emphasize that everything relating to security comes down to individual choices. No matter the area of Bitcoin we’re talking about, there’s always something one person can do. I repeat that line like a mantra. I hope it’s what every reader remembers.


    JB: What was the writing process like? A little here or there amid life, or chapters written in long, intensive writing sessions?

    LW: I had the outline extremely early on. Apart from some minor refinements, this book existed in my head six months ago. The process was all about going from outline to first draft, then polishing the drafts, iteratively. My notes folder has 10 revision cycles, and each one I focused on different areas, including making everything more consistent.

    Full disclosure: I used AI to keep me organized. I would ask it to check if I was describing some concept inconsistently, or to make sure that each chapter included the same sorts of structural elements. Even though I planned these things out myself, inconsistencies crept in. It was also an invaluable fact checker, keeping me honest whenever I made claims that wouldn’t hold up under scrutiny. I never used AI to actually do any writing. It was all me. But I probably would either have produced a less coherent book or done it more slowly without AI assistance.

    In any case, this consumed my life for six months. I obsessed over it, and worked hard to make sure every detail was correct. I’m proud of the end result.


    Through going on podcasts and discussing Defending Bitcoin with others, I realize that maybe I could have emphasized a certain point better, or that I missed something I really should include later. But I’m confident that the book, as it is, gives anyone who reads it the tools to be more confident about Bitcoin security, and about the outlook for Bitcoin in general.


    Defending Bitcoin: Industrial-Grade Cybersecurity for the Monetary Grid is out June 15, and you can find early copies at BTC Prague this week.